


















Trace a CNAME lookup from the alias to the final destination
Trace a CNAME from hostname to target, check the final address records, and recognize alias loops or missing targets. Keep DNS aliases separate from redirects.
 Written byYiyao
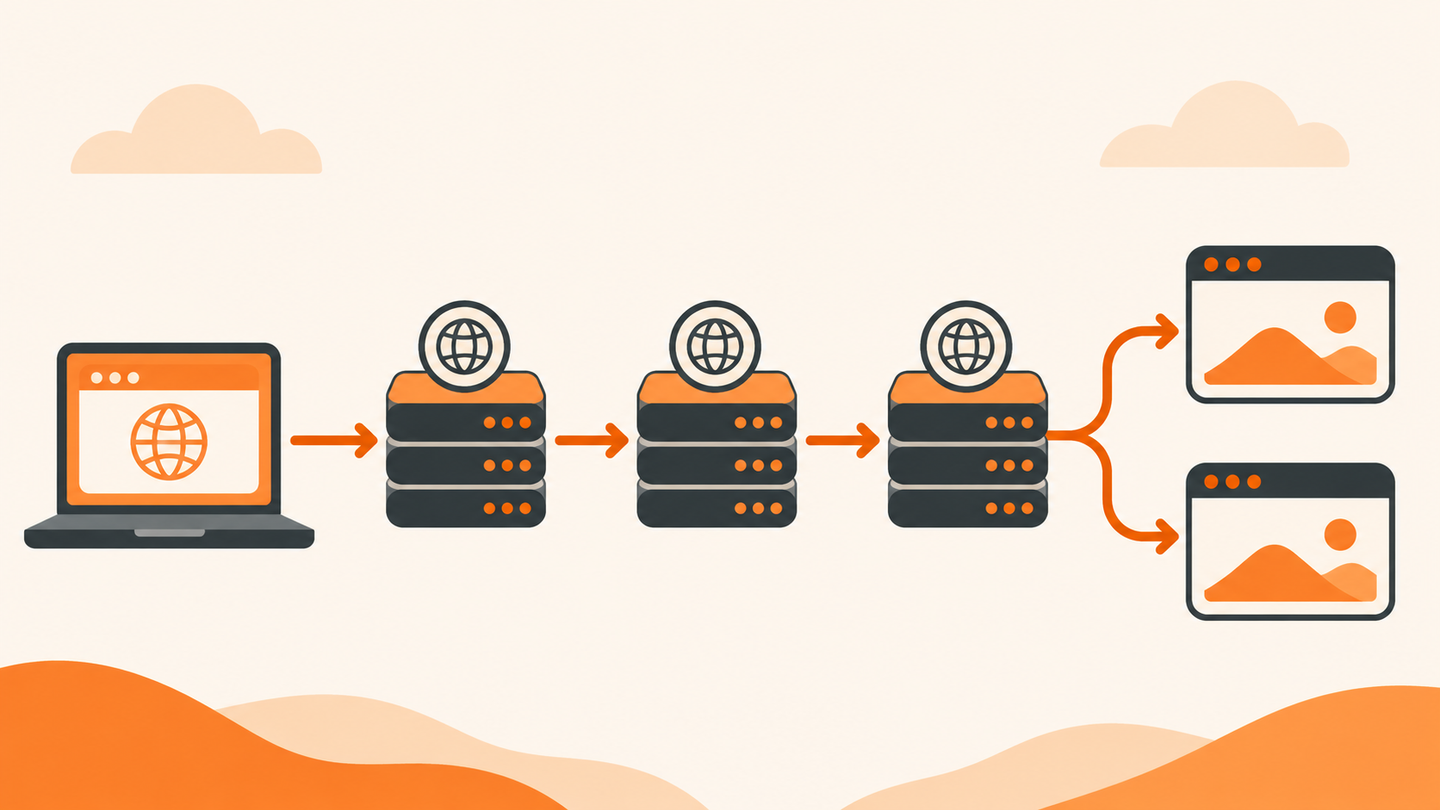
A CNAME points to another name
A CNAME record declares one DNS name to be an alias of another. Its value is a hostname, not an IP address or a complete web URL. To understand where a browser can connect, inspect the alias and the target's address records.
A CNAME does not instruct a browser to replace the URL in its address bar. HTTP redirects are a separate application behavior. This distinction matters when a branded domain points to a hosted platform but still needs correct hostname routing and a valid certificate.
Query the alias and follow the actual answer
nslookup -type=CNAME www.example.com
nslookup -type=A www.example.com
nslookup -type=AAAA www.example.com
These commands demonstrate the query shapes using a public example name; they do not promise that it currently has a CNAME. For a domain you control, use the exact alias supplied in the service setup instructions.
If the CNAME answer identifies a target, copy that returned name into an address query. Preserve each step of the chain. Some DNS providers implement alias-like features by returning flattened A or AAAA answers, so an absent CNAME does not by itself prove a service mapping is broken.
Read a short illustrative chain
| Name | Type | Value |
|---|---|---|
| shop.example.com. | CNAME | edge.example.net. |
| edge.example.net. | A | 192.0.2.20 |
| edge.example.net. | AAAA | 2001:db8::20 |
These documentation names and addresses describe an invented chain. The first row is the alias relationship; the next rows are address destinations. If the target changes its address while the alias remains stable, future resolution follows the target's current published data, subject to caching.
Record the TTL of each relevant answer. The alias and its target can have different cache lifetimes. A single TTL shown beside one row is not a guaranteed time for every client and every step to refresh.
Find the point where the chain fails
| Result | Investigation |
|---|---|
| Alias exists; target reports NXDOMAIN | Check the target spelling and whether the service still owns it |
| Two names refer back to each other | Remove the loop through the authorized DNS change process |
| Target resolves; HTTPS fails | Check the certificate, hostname mapping and service availability |
| No CNAME; A or AAAA answers exist | Check whether direct or provider-flattened mapping is intended |
Do not repeatedly create new aliases to work around a missing upstream target. Confirm the correct service destination with the provider. Avoid claiming an unused third-party hostname simply because you discovered a dangling record; report the issue to the authorized owner. If a missing target returns NXDOMAIN, follow the NXDOMAIN troubleshooting guide before changing the alias.
Check record coexistence before editing
A conventional CNAME cannot share its owner name with ordinary records such as A or MX. The zone apex also needs its SOA and NS data, so a normal CNAME at that name is usually unsuitable. Follow the DNS provider's documented apex-alias mechanism when one is required.
Keep provider-specific ALIAS, ANAME, or flattening behavior separate from the standard CNAME result. The public query may show only addresses. Check both the provider configuration and the public response before changing a record that appears to be missing.
Validate the user journey after DNS
Open the intended HTTPS hostname from the affected environment after the DNS chain is understood. Confirm that the certificate covers that hostname and the page belongs to the expected site. A correct alias can still lead to a platform error if domain verification is incomplete.
Use Arcvenza NSLookup for an independent public observation and keep the node, query mode, timestamp, and record type. Follow the HTTP error guide when DNS succeeds but the server returns an application error. This keeps the fix at the layer where the failure occurs.
FAQ and next action
Does a CNAME create a 301 redirect? No. Configure permanent redirects at the HTTP layer.
Why does the DNS control panel show an alias but the lookup shows addresses? The provider may flatten the answer. Verify its documented behavior and the resulting service. Start with one exact name and trace every returned target before making a change.
Technical references
RFC 1034: Domain names · RFC 1035: DNS records · Microsoft: nslookup
RFC 1034: Domain names · RFC 1035: DNS records · Microsoft: nslookup